
Hello everyone! I am the victim of the $4.56 million theft on Aster. My account experienced abnormal transfers around early morning Beijing time on November 13, 2026, resulting in a total loss of $4.56 million. Here are the detailed events of this incident. @Aster_DEX @cz_binance @heyibinance @Leonard_Aster
@binance @BNBchain @YZiLabs @0xVeryBigOrange @cryptobraveHQ
@star_okx @Cryptosis9_OKX @Bitfatty @BlockBeatsAsia @giantcutie666
I didn't sign a single transaction, and my wallet private key wasn't lost, yet my money is gone! I demand that Aster compensate me with the original assets.
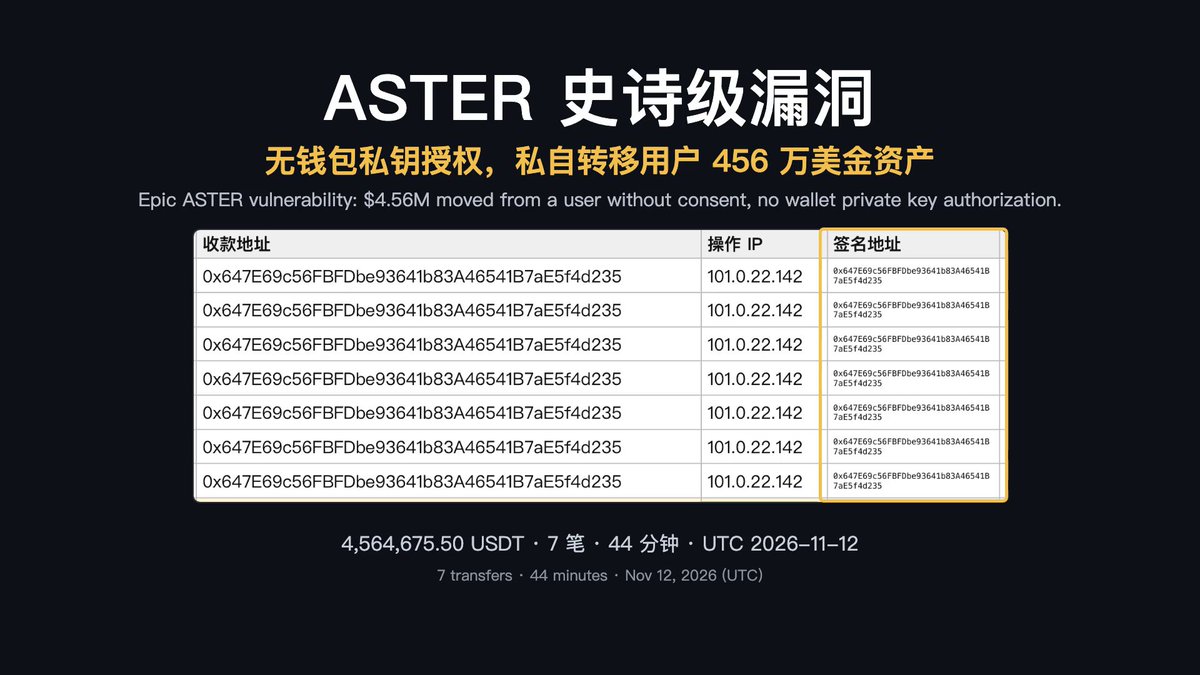
The "Agent Key" automatically generated by the Aster website transferred 4,564,675.50 USDT from my account to a newly registered stranger's account, and 33 BTC were also sold at market price. According to Aster's own rules, none of these 7 transactions should have been allowed.
Every point below comes from records provided by Aster to me, Aster's written explanations, official documentation, and public on-chain data. All times are UTC.

1. What Happened
On November 12, 2026, over exactly 44 minutes. At 16:22, someone used this agent key to register a new account; from 16:24 to 17:08, Aster's system executed 7 "Transfer to Other User" transactions following its signature, moving all $4.56 million into that new account.

My own account records clearly show (screenshots display web timezone, here using UTC): From 16:22 to 17:07, there were 9 transfers back and forth between contracts and spot, moving all 33 BTC into spot; from 16:49 to 16:59, they were split into 17 market sell orders; the proceeds, along with my original USDT, were then moved out by those 7 transfers. Not one step was done by me, and Aster did not block a single one!


2. It Wasn't Signed by Me, Nor Was It My Wallet Private Key
Aster's own signature records state: The signing address for all 7 transactions was the agent key 0x647E, not my wallet.

Even Aster's CEO initially concluded in the group chat that "the agent key was exposed, not the address's own private key."
Later, Aster's CEO confirmed in writing in the coordination group: This key is "a temporary private key created locally after obtaining wallet authorization in the browser, not the user's own wallet private key."

I was unsure at first; later I saw that after this key expired, subsequent login attempts by the attacker failed, and the remaining funds were untouched. If the wallet private key had truly been lost, not a cent of the remaining funds would have been safe!

3. The Key and Permissions Were Given by Aster
This key is called @aster-desktop, automatically generated by the Aster website when I clicked "Enable Trading"; it must be enabled for every user trading on the web. I always traded manually, never used quant strategies, and didn't even know this key existed, let alone that it could transfer my money to others!

Aster told me in writing: This key uses default web permissions, includes "Fund Transfer," but does not include Withdrawal.
However, the permission column for it on the web only showed Read, Contract Trading, and Spot Trading—there was no "Fund Transfer." I never selected it, nor could I see it! Less than 6 hours after the incident, Aster changed the default to disallow transfers to other accounts. If there was no problem, why change it?

4. According to Aster's Own Rules, None of These 7 Transactions Should Have Been Allowed
Aster's API documentation states: Transferring assets to another user (Transfer to Address) is classified as WITHDRAW level, documented since May 2026. Aster also stated in writing that this key has no withdrawal permissions. How could a key without withdrawal permissions execute 7 withdrawal-level transfers?
Aster's documentation also states: For compliance, internal transfers to other users are not allowed when Privacy Mode is enabled. I enabled it on September 16 and never disabled it; there is no record of disabling it in the Aster chain explorer.


When I tried to transfer out myself, the web prompted "Please disable User Privacy Mode," blocking it properly; yet those 7 transactions went through one by one! Did they not follow their own written rules?

5. The System Never Blocked It Once
A new account registered just 113 seconds prior received 700,000 USDT; withdrawals began within 3 minutes; the receiving address was the signing key's own address. In 44 minutes, $4.56 million moved, with zero blocks, zero delays, and zero alerts. Isn't this absurd?

6. Where Did the Money Go?
The new account withdrew 4,564,674.38 USDT in 10 transactions. After cross-chain bridging, 1,000 ETH entered Tornado Cash, and 768.1 ETH and 993,999.67 USDT entered NEAR Intents confidential swaps. Whether or when recovery is possible is uncertain. I will fully cooperate with the investigation and have kept every on-chain hash; but compensation should not wait for recovery: if recovered, the funds belong to Aster after they compensate me.

7. This Is Aster's Responsibility
The key was generated by the Aster website, the permissions were granted by Aster's defaults, the rules were written by Aster, and the transactions were approved by Aster's system. Regardless of who held the key, according to Aster's own rules, it should not have been able to move my money.

My Demands
1. Provide a written resolution plan with a specific date;
2. Compensate with original assets: 33 BTC, 2,200,134.21 USDT, plus forced liquidation fees, without waiting for recovery;
3. Explain which permission authorized these 7 transactions; the requests did not contain my address, so how did you deduct funds from my account;
4. Preserve all logs.
All I want is to get my assets back! #Aster @Aster_DEX @cz_binance @heyibinance @Leonard_Aster


